Considering Cybersecurity as Cloud Work Expands

When the pandemic forced many business users to move to remote work, it also forced the network security “boundary” to expand greatly and with great speed. Companies quickly adapted their tools and work so that it could be done somewhat effectively even as the employee working environment changed.  But new security models to match with new working models have not as quickly been adopted.

Business cloud workloads grew, by some estimates, as much as 20% just in the first 6 months of 2020. Yet many of those businesses electing to bring cloud working models to their business also made of the mistake of not expanding their security as they expanded the cloud network. This leaves systems and information vulnerable. Phishing, ransomware, credential theft and web app attacks have increased, catching businesses in their vulnerable states.

“In April to June of 2020 alone, security incidents increased by 188%.”

Even more than on-premises systems, it was the external cloud-based data and applications that were under attack because so many companies expanded their use of cloud services without enhanced security as part of the plan. Any expansion to include the cloud as network also significantly increases security risks. One report found that 35% of businesses made their cloud storage openly accessible to the public, allowing anyone to access it via the internet.

Don’t let your critical information be exposed or put at risk. When you begin using a cloud service, make sure to also address security for the new working mode or it could lead to lost or leaked information or a system breach.

Mendelson Consulting and NOOBEH cloud services take security very seriously. We help our clients keep their applications and data working properly and have a focus on methods to keep information safe regardless of what cloud you work on.

jm bunny feetMake Sense?

J

1 ( https://duo.com/blog/growing-security-safely-in-canada )

Update your Mac to keep getting Office application updates

Microsoft’s upcoming November 2020 update has some direct impacts to users running macOS, especially if running macOS 10.31 or earlier. As of November 10, 2020, existing Microsoft 365 for Mac users running macOS 10.13 or earlier will not receive any further Office application updates. If the machine is upgraded to macOS10.14 or later, updates will be allowed to proceed on that computer.

With the Microsoft 365 for Mac November 2020 update, users running macOS must be running 10.14 Mojave or later in order to continue to receive updates for Office applications, and any new installs of Microsoft 365 for Mac will require macOS 10.14 or later.

Word, Excel, PowerPoint, Outlook and OneNote are the applications included which will no longer receive updates – including security updates – if the macOS they’re running on is too outdated.

Among the benefits of using Microsoft 365 is that the software is always kept up to date, including enhancements and new features as well as security and safety updates that help keep the software (and the associated data) more secure. You may continue with the older version of macOS, and your Office applications will continue to work. But losing out on updates not only keeps you from benefitting from the most current capabilities of the software (and getting full value from your subscription), but it also puts your security and compliance at risk.

Microsoft 365 applications are continuously updated with new features, connected services and enhancements to security. Modern operating system platforms are necessary to support some of these improvements, requiring users to update their computer operating systems as well as the applications running on them. With the Microsoft 365 November update, Mac users need to be running one of the three most recent versions of macOS to keep their Office applications recent, too.

Make Sense?

J

Building A Solid Foundation for Business Cybersecurity

The cybersecurity threat landscape has changed dramatically in the last few years. No longer primarily a big-business concern, cybersecurity has become a key focus of businesses small and large. Attacks on SMBs are on the rise, perhaps because they represent a plentiful and often easy target. And the cost of damage and disruption to business just keeps going up.

Cybersecurity is not a problem you can simply throw a bunch of money and tools at to fix.

No matter how much great software or fancy systems you implement, the people will always be a big part of the equation. The root cause of over half the data breaches reported is a result of negligent employees or contractors.

That means that nearly half of all attacks are being executed through phishing or social engineering. The only tool you can apply to this problem is education. Efforts should be focused on security awareness and training workers to be more cautious to the point of almost being paranoid. Better to be safe than sorry in this case.

Training workers to be more careful as they work with emails, documents and websites is part of it, but there is much more to making sure the business is addressing the entire cybersecurity issue. NIST (National Institute of Standards and Technology) offers a wide variety of information and guides that businesses can use to learn more about and implement cybersecurity practices. Among these resources is the Cybersecurity Framework.

According to NIST, “the Framework focuses on using business drivers to guide cybersecurity activities and considering cybersecurity risks as part of the organization’s risk management processes.” It is a highly useful tool in helping the business align and prioritize activities with business requirements, risk tolerances and resources. The standard framework includes elements that are consistent and common across sectors and critical infrastructure, so it can be oriented to any business.

Even if the business is not prepared to delve into the details of a comprehensive cybersecurity policy and guideline, a basic outline and approach cannot be avoided without asking for disaster.

Putting this squarely into the Risk Management category, there is an ongoing process of identifying, assessing, and responding to risk situations or conditions. To manage the risk, businesses need to consider the likelihood that an event will occur and what the potential impact is as a result.

Knowing the acceptable level of risk for reaching the business objective is the risk tolerance. If a business understands its risk tolerance, the company can prioritize cybersecurity activities and make informed decisions about cybersecurity expenditures.

There are five key functions to consider as it relates to cybersecurity risk: Identification, Protection, Detection, Response and Recovery. How the business addresses each of these in the context of the systems and activities is essentially the business’s cybersecurity posture, a high-level and somewhat strategic view of the organization’s management of cybersecurity risk.

The key to building a solid foundation for  business cybersecurity practice is to establish a platform where all the business applications and data can be identified and access secured.

User desktops, productivity applications, operational software and business data can be hosted on private cloud servers, allowing the business to fully-manage data and application access. The server-based model reduces or eliminates the need to sync data to devices, and remote desktops keep user environments secure, patched and up-to-date.

Our consultants can’t write your cybersecurity policies or determine your risk tolerance, but we can help implement a solution that improves fault tolerance, resilience, and recovery.

Make Sense?

J

Strong Passwords and MFA : It’s All About the Bots

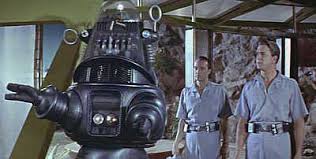
Robbie the Robot from movie Forbidden Planet

You may have noticed that more online services are requiring strong passwords – cryptic phrases or letter combinations along with symbols and numbers – and Multi-Factor Authentication (MFA). The goal is to keep services more secure than a simple password allows.

These service providers have recognized that their services are far more secure when the user has to prove they are who they are, and prove it in more than one way. A password plus a special code texted to your phone, or maybe an email to your backup email account are examples of MFA. This means that the password alone isn’t good enough to gain access; the user must satisfy an additional challenge to confirm their identity.

Why is this additional level of account security a good idea? BOTS, that’s why.

A bot is a software application that is programmed to do certain tasks. Bots are automated, which means they run according to their instructions without a human user needing to start them up. Bots often imitate or replace a human user’s behavior. https://www.cloudflare.com/learning/bots/what-is-a-bot/

Bot (like roBOT) does what you tell it. Give it instructions and it runs. Give it some rules to follow and actions to perform when certain conditions are met and off it goes.

The problem with bots is that not just the good guys use them. Bad guys use them… a lot.

Bots can send emails, engage in chats and help you reset your password. They can also carry out cyberattacks at a pace that no human could match. Bots will search for public IP addresses, they’ll pummel an address with intrusion attempts and logins and may keep trying until they’re either successful or they give up. Bots are very good at brute force, because they have all the patience they need. It’s software, so it doesn’t get tired or bored and it can be programmed to not give up.

This is among the reasons for Noobeh’s strict password policy and why we strongly recommend our clients don’t store their passwords to make connecting to the service faster and simpler. Fast and simple is good but not where security is concerned. Our goal is to not only keep your applications and data available for anytime/anywhere access, we want to keep your cloud environment secure and as safe as possible.

Contact us today to get the cloud hosting platform your business needs, along with the privacy and security features the Microsoft Azure platform can provide. Keeping your systems secure isn’t just about keeping your secret password a secret. It’s about putting in place the best methods possible to ensure that your account doesn’t get compromised because a bot guessed your pet’s name.

Make Sense?

J

Are You Prepared for SQL Server 2008 End of Support?


Everything gets old eventually, and now it is official for SQL Server 2008.

03-2012sean-phone-328-e1377042261105On July 9, 2019, support for SQL Server 2008 and 2008 R2 will end. That means the end of regular security updates and general support for the product. Are you ready?

It took more than 10 years for Microsoft to end support for our beloved SQL 2005 and version 2008 has enjoyed a similarly long reign. But it’s over and you need to get used to the idea. Even more, you need to get upgraded to a new version of SQL so your systems can still be patched, updated and supported. With all the nasty exploits out there, letting your software get out of date is more of a business risk than ever.

With cyberattacks becoming more sophisticated and frequent, running apps and data on unsupported versions can create significant security and compliance risks. The 2008 family of products was great for its time, but we highly recommend upgrading to the most current versions for better performance, efficiency, and regular security updates.

Now is a Good Time to Consider Azure

Microsoft is giving a present to businesses that want to migrate their workloads to Azure. For those customers that elect to take this as an opportunity to move to the Azure cloud, extended security updates will be available for free in Azure for 2008 and 2008 R2 versions of SQL Server and Windows Server to help secure workloads for three more years after the end of support deadline. Moving existing systems to the Azure cloud is a natural step in modernizing the business infrastructure and makes the next step of upgrading to managed database services and/or migrating to new Azure servers a lot easier.

Upgrading isn’t simply a matter of maintaining status quo, either.

Moving to new versions can be a foundation for new strategic capability and increasing overall business potential, powering new decision-making processes fueled by analytics and business intelligence.

The Microsoft Lifecycle Policy offers 10 years of support (5 years of regular support and another 5 years of extended support) for the 2008 and 2008 R2 versions of SQL Server and Windows Server. When the extended support period ends, there will be no patches or security updates, which always creates security risk.

If your business is going to remain competitive, you can’t rely on outdated systems.

Your business is tough enough to manage without having your systems work against you.  Software that prevents you from keeping up with demand, creates risk in compliance and security, and reduces operational performance is not what you need. Collecting, storing and rationalizing data takes power and speed, and securing your growing information warehouse requires vigilance in security and update management.

Use this opportunity to review your platforms and applications, and consider moving your on-premises or co-located systems to the cloud. The upcoming milestone is a great opportunity to transform applications and infrastructure to take advantage of cloud computing and the latest versions of SQL Server and Windows Server.

jmbunnyfeetMake Sense?

J

Contrary to What You Learned in Grade School… Sharing is Bad, Okay?

There is a place and time for sharing. Share your color crayons, share your toys… share your feelings with those you love. But when it comes to business technology and infrastructure, sharing isn’t always the best approach. Some things you should just keep for yourself… like the servers you use for hosting business desktops, desktop applications and business data.

When we first began the journey of bringing small business desktops and applications like QuickBooks to the Internet, the “cloud” was not yet a thing. Hosting providers put up servers in racks in data centers, installed software and stored data on behalf of customers, and did their best to find ways of making the service affordable. Elastic resources, massive scalability and built-in redundancy (which are benefits of a real cloud fabric) were not generally available nor were they even remotely affordable. Because the hardware, networking and other resources that make up the hosting infrastructure is costly, it is important for the hosting service provider to be able to spread those costs across the entire customer base.

In most cases, this meant creating shared servers where many customers run their applications and store their data. Even when a provider suggests that a customer has a “private” server, there is still a good chance the server is using shared storage and/or networking resources made accessible in the environment.

Sharing can be a good thing or a bad thing, and it often depends on the behavior of those involved. In shared application hosting environments, particularly desktop hosting environments, there is a lot of potential for intentionally and unintentionally causing problems that can and will impact other users and customers on the platform.

A simple provisioning error might allow a user to see data belonging to another company or have access to applications or services they should not.

With shared resources, bad actors and intruders can often escape permission boundaries, attaching to network shares and other computers on the platform.

Malware accidentally introduced by an innocent user from one company could easily penetrate the entire system, following paths to data storage locations and other servers, spreading the problem to many customers and systems and even data centers.

If you are operating on the compromised system you are at risk, even if the compromise wasn’t initiated by one of  your users or from within one of your applications.

In the realm of QuickBooks hosting providers, the issues around sharing infrastructure and resources have created some very difficult situations for hosts and for their customers alike – especially when it comes to dealing with computer viruses, malware and ransomware. A few high-profile events, as well as numerous incidents which have flown under the radar, have revealed just how damaging the shared approach can be.

With the IRS, AICPA and other agencies issuing increasingly strong guidance for tax and accounting professionals to protect client information, finance professionals should strongly consider the risk introduced through shared hosting service arrangements and evaluate if it is greater than the costs of having a more private system.

Cloud platforms available today are fully matured, delivering scalability and agility at price levels that are affordable even for very small businesses.  No longer solely for enterprise enjoyment, real cloud solutions and delivery models can be used by small businesses for desktop and application hosting without compromise. Every business deserves their own cloud, and we know how to make that affordable.

Cooper Mann works with teams deploying on the Microsoft Azure platform, offering an agility in design not previously available with legacy computing approaches. Because every delivery is absolutely private to each customer, the solution can be scaled up (or down!) on demand to suit the specific needs of the individual business. More important is the fact that each customer operates separately, so any bad behavior the system may suffer from is their own.
jmbunnyfeetMake Sense?

J